What good is a backup you have never tried to restore? That question sounds almost rude, but it is the one that separates real data protection from a comforting dashboard with a green checkmark. Plenty of teams have learned this the hard way: the backup job ran nightly for two years, the alerts stayed quiet, and then a ransomware event or a failed disk turned a routine Tuesday into a very long weekend. The problem was not the software. The problem was that nobody had ever opened the backup and pulled a file back out. (Backup (Wikipedia))
Cloud backup tools sit in a crowded, noisy market. Every provider promises encryption, versioning, and “set it and forget it” simplicity. The useful skill is not memorizing product names. It is knowing what questions to ask, what the underlying storage actually does, and where the cost traps hide. This article walks through that, from the basic rule of thumb that has survived for twenty years to the compliance clauses that decide whether your backup is even legal.
What cloud backup tools actually do, and what they don’t
A cloud backup tool copies your data to storage you do not own, keeps multiple versions over time, and lets you restore a specific point in the past. That is the whole job. Everything else, from deduplication to dashboards, is a feature layered on top.
The most common mistake is confusing three things that sound alike:
| Type | What it does | Typical trap |
|---|---|---|
| Backup | Keeps versioned, restorable copies over time | Untested; restores fail or take days |
| Sync | Mirrors changes across devices in near real time | A deletion or ransomware encryption propagates instantly |
| Cloud storage | A bucket or drive you manage yourself | No scheduling, no versioning unless you configure it |
Sync is not backup. If a file is deleted or encrypted on your laptop, a sync service faithfully deletes or encrypts the copy in the cloud within seconds. Many small businesses discover this only after an incident. The fix is blunt: treat sync as a convenience layer for working files, and run a separate, versioned backup with retention you control.
The other thing backup tools do not do is decide what matters. A tool will happily back up 40 terabytes of duplicated video assets and skip the one database that runs payroll, unless someone tells it otherwise. That decision is an inventory question, and it is worth doing properly before you buy anything. A structured approach to what to inventory before a cloud migration applies just as well to backup scoping: systems, owners, data classifications, and recovery priorities.
The 3-2-1 rule still earns its reputation
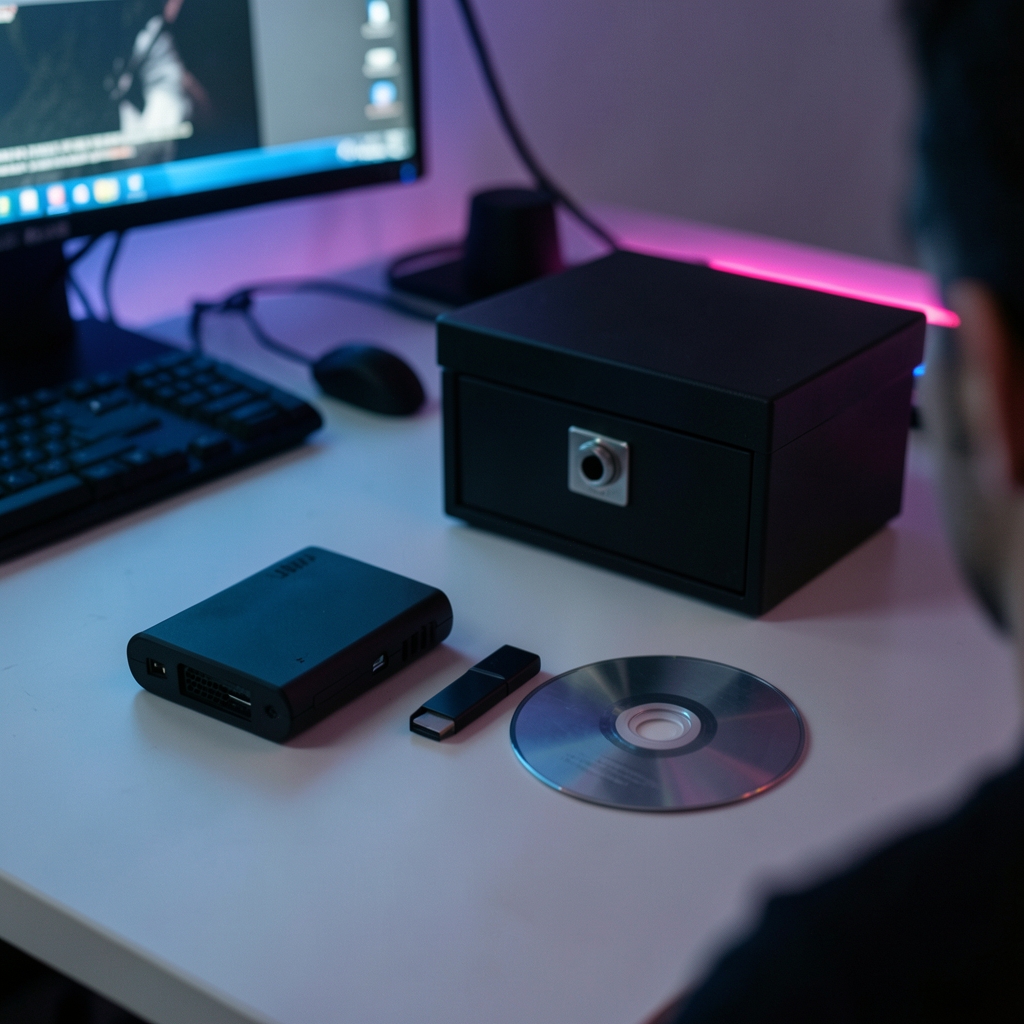
The 3-2-1 rule says keep three copies of your data, on two different types of media, with one copy off-site. It is usually credited to photographer Peter Krogh, who popularized it in the mid-2000s for digital photo archives. The attribution is commonly cited rather than independently verified, but the logic holds regardless of who said it first.
Why does it still work? Because it defends against different failure modes at once. Three copies covers accidental deletion and corruption. Two media types covers a single class of hardware failure or a bad batch of drives. One off-site copy covers fire, flood, theft, and a ransomware crew that encrypts every reachable network share.
A modern reading of 3-2-1 adds two refinements. First, one copy should be immutable or offline, meaning it cannot be altered or deleted even by an administrator with valid credentials. Object lock features, which let you set a retention period that blocks deletion, are the usual way to do this in cloud storage. Second, one copy should live in a different account or provider than your production environment, so a compromised credential does not reach both. That separation is the same principle behind splitting workloads across cloud accounts, applied to your safety net.
Backup is a contingency plan, not a feature
If you work in a regulated environment, backup is not an IT preference. It is a documented requirement.
The HIPAA Security Rule, at 45 CFR §164.308(a)(7), sets a contingency plan standard that includes a data backup plan and a disaster recovery plan. In force since 2003, with later amendments, it applies to covered entities and their business associates in the United States. On the European side, GDPR Article 32 requires appropriate technical and organizational measures, and it explicitly names a process for regularly testing, assessing, and evaluating the effectiveness of those measures. Whether backups fall inside that clause is an interpretive question that varies by regulator, but reading them as out of scope is a risky bet.
NIST publishes the reference documents most practitioners end up citing. NIST SP 800-34 Rev. 1, the Contingency Planning Guide for Federal Information Systems, treats data backup as one component of a broader contingency plan rather than a standalone checkbox. NIST SP 800-209, Security Guidelines for Storage Infrastructure, covers security considerations specific to storage systems, including cloud storage. Both are worth skimming once, because auditors tend to speak their language. (NIST Cybersecurity overview)
The practical takeaway: write down your recovery objectives. Recovery point objective (RPO) is how much data you can afford to lose, measured in time. Recovery time objective (RTO) is how long a restore may take. A tool that backs up every hour but takes three days to restore a 5 TB dataset may fail your RTO no matter how good its marketing is.
What actually works in practice
These are the habits that separate teams with working backups from teams with backup software.
Test restores on a schedule, not after an incident
Pick a cadence and stick to it: monthly for critical systems, quarterly for everything else. Restore a random file, restore a whole directory, and once a year restore an entire system to a clean environment. Record how long it took and compare it to your RTO. If the numbers do not match, either the objective or the tooling needs to change.
Watch the restore cost as well as the storage cost
Object storage pricing is famously asymmetric. Storage is cheap; getting data back out often is not. Many providers charge egress fees for downloading data, which means a full restore during an emergency can generate a bill in the thousands of dollars. Pricing specifics change constantly, so check current rates rather than trusting a blog post. A clearer way to think about this is to track cloud data transfer costs alongside storage, so the restore line item is visible before you need it.
Understand where encryption happens
Client-side encryption means data is encrypted before it leaves your machine, so the provider stores ciphertext it cannot read. Provider-side encryption means the vendor holds the keys. Both can be legitimate, but the second gives the provider, and anyone who compels the provider, a path to your data. Whether a specific tool does client-side encryption is a per-product fact you have to verify in its documentation, not something to assume from a marketing page.
Keep credentials separate
Backup systems are a favorite target because they hold everything. Use a dedicated account, separate credentials, and multi-factor authentication. If your backup tool uses the same admin identity as your production environment, a single phishing email can reach both.
Write runbooks a tired person can follow
At 2 a.m. during an outage, nobody wants to reverse-engineer a retention policy. Write the restore steps down, name who can authorize a restore, and keep the document somewhere that does not depend on the systems being restored.
Comparing cloud backup tools without getting lost
Vendors segment the market in ways that mostly reflect their pricing model rather than your needs. A rough map helps.
| Category | Best suited to | Watch for |
|---|---|---|
| Endpoint backup | Laptops and desktops, remote teams | Per-device pricing; slow restores of large profiles |
| SaaS-to-SaaS backup | Mail, chat, and document platforms | Assumes the platform’s own retention is enough, which it usually is not |
| Server and database backup | Virtual machines, SQL, object stores | Agent sprawl; restore of a single item is often awkward |
| Cloud-to-cloud backup | Workloads already in one cloud | Egress costs on restore; limited cross-region options |
| Hybrid appliances | Large on-premises estates | Hardware refresh cycles; local cache sizing |
A sensible evaluation process looks like this:
- List the systems and data classes you must protect, with an owner for each.
- Set RPO and RTO per class, not for the whole company.
- Shortlist three tools and ask each for its restore documentation, not its sales deck.
- Run a timed test restore of a realistic dataset before signing anything.
- Check the exit terms: can you get your data out, in what format, at what cost?
- Confirm the compliance clauses you actually need, in writing.
Step five is the one people skip. A backup vendor that makes export difficult has effectively made your data hostage. Ask for a sample export before you commit.
Where architecture decisions creep in
Backup rarely stays a standalone purchase. It touches region choice, account structure, and cost governance, and those three interact. Region selection affects latency, legal jurisdiction, and price, and the announcements that describe new regions are written for investors as much as engineers. Learning to read a cloud region announcement for what it actually says about data residency is a genuinely useful skill here.
Cost governance matters too, because backup bills grow quietly. Storage accumulates, retention windows drift longer than policy allows, and orphaned snapshots linger for years. Reviews that only show a total spend number are useless to the people who can fix it. Making cloud cost reviews useful to engineers means showing per-system, per-owner numbers with a clear action attached. Teams that build this discipline early spend far less on backup than teams that discover it after an audit.
Conclusion
Cloud backup tools are not complicated in concept. Copy the data, keep versions, store a copy somewhere else, and prove you can get it back. The complexity lives in the details: sync masquerading as backup, egress fees that turn a restore into a budget event, encryption keys held by someone else, and retention policies nobody has read since setup.
Start with the boring parts. Inventory what you have. Set an RPO and RTO you can defend. Enforce 3-2-1 with one immutable copy. Then test a restore and time it. If the numbers hold up, the tool choice matters far less than the discipline around it. If they do not, no amount of dashboard polish will save you.
Frequently asked questions
Is cloud backup the same as cloud storage?
No. Cloud storage is a place to put files, and you manage versioning and retention yourself. Cloud backup is a process that automatically copies data on a schedule and keeps multiple restorable versions. A storage bucket can be part of a backup strategy, but it is not one on its own.
How often should backups run?
It depends on your recovery point objective, which is how much data you can afford to lose. If losing a day of work is tolerable, nightly is fine. If it is not, you need more frequent runs or continuous protection. Set the objective first, then choose the schedule that meets it.
Why do sync tools fail as backups?
Because sync propagates every change, including deletions and encryption. If ransomware encrypts files on a laptop, a sync service uploads the encrypted versions within seconds and may remove the clean copies. Backup tools keep historical versions that a sync tool typically does not.
Do I need to test restores if the backup job reports success?
Yes. A successful backup job only confirms that data was written somewhere. It says nothing about whether the data is readable, complete, or restorable within your time target. Regular test restores are the only reliable proof.
What is the 3-2-1 rule?
Keep three copies of your data, on two different types of media, with one copy stored off-site. It is a simple framework that covers accidental deletion, hardware failure, and site-level disasters at the same time. Many teams add a fourth element: one copy that cannot be altered or deleted.
Are cloud backups enough for compliance?
Not automatically. Regulations typically require documented plans, defined recovery objectives, and evidence that you test them. A backup tool provides the mechanism, but the plan, the testing record, and the retention policy are what auditors actually review.








