Quick Answer: How does public cloud work?
Public cloud works by pooling physical servers, storage, and networking inside large data centers owned by a provider, then slicing that hardware into virtual resources that many customers rent at the same time. A software layer called a hypervisor keeps each customer’s workloads isolated, while automation handles provisioning, scaling, and metering. You sign up, request resources through a console or API, and pay only for what you consume.
The main alternative is private cloud, where one organization runs dedicated infrastructure for itself, and hybrid models that connect the two. Public cloud differs by being open to any customer, shared across tenants, and billed on usage rather than owned outright.
Before committing, compare isolation guarantees, region and zone coverage, network egress charges, compliance certifications, support terms, and how metering is calculated.
What “Public” Actually Means in Cloud Computing
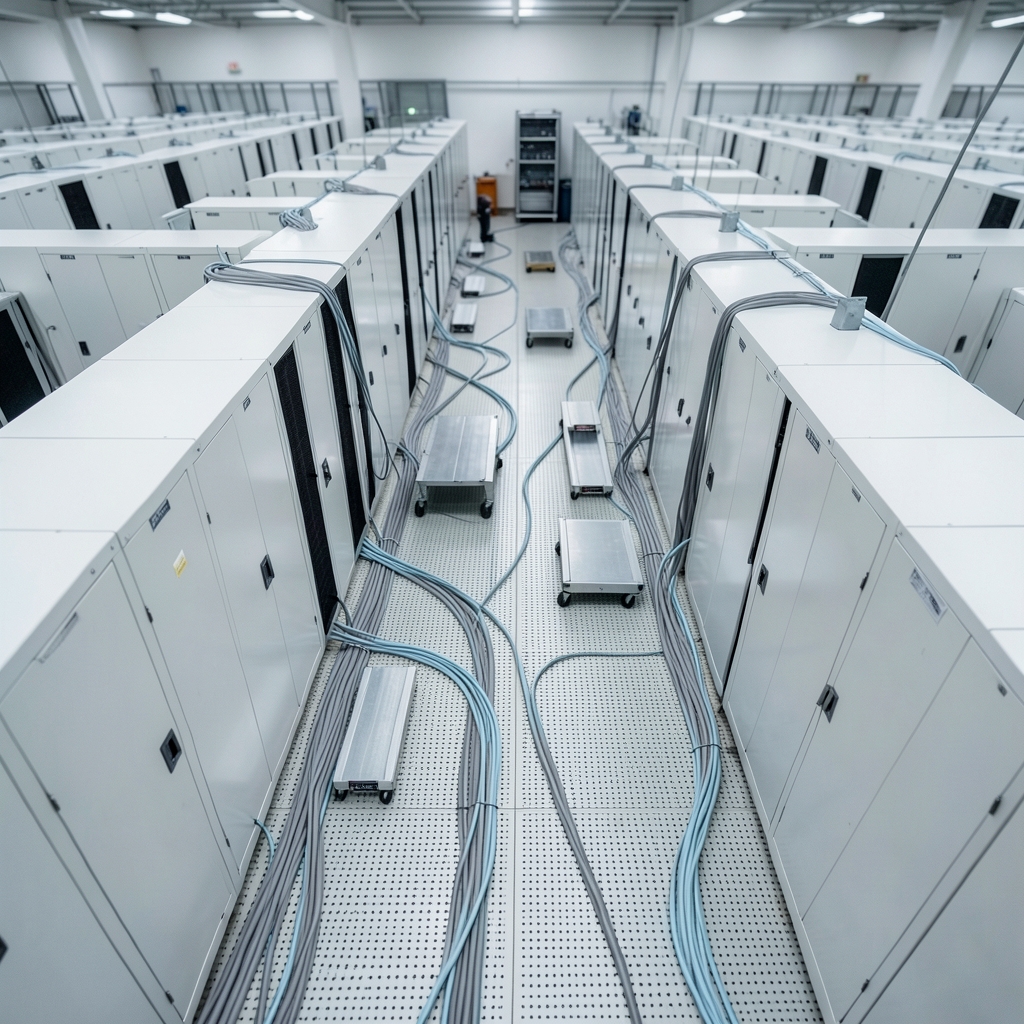
Picture a massive warehouse full of servers. Now imagine hundreds of companies renting space on those same machines, each one convinced it has the place to itself. That illusion, carefully engineered, is the heart of public cloud.
The most widely cited definition comes from a U.S. government standards body, which describes cloud computing as a model for enabling on-demand network access to a shared pool of configurable computing resources that can be provisioned and released with minimal management effort. That same framework names four deployment models, and public cloud is the one where infrastructure is provisioned for open use by the general public and owned by the provider.
Here is where language gets slippery. In everyday business talk, “public cloud” usually just means “a hyperscaler’s platform.” In standards terms, it means anyone can sign up. Those two ideas overlap most of the time, but not always.
The Machinery Underneath: Virtualization and Multi-Tenancy
Strip away the marketing and public cloud is virtualization at industrial scale. A hypervisor sits between the physical hardware and the operating systems running on it, carving one server into many virtual machines. The concept is old, tracing back to IBM’s CP-67 work in the late 1960s, but it only became cheap and mainstream on commodity x86 hardware in the 2000s.
That one mechanism makes the rest possible. Because the hypervisor can start a virtual machine in seconds, providers can sell capacity by the minute. Because it enforces boundaries, thousands of customers can share the same rack without reading each other’s data.
Multi-tenancy is the business model built on top of that isolation. Providers spread many customers across shared hardware to keep utilization high, which is why public cloud can undercut the cost of running your own small data center. Isolation is enforced through hypervisors, virtual networks, and identity controls. The exact implementation varies by provider and is not standardized, so if you handle sensitive data, ask specific questions about how separation is achieved rather than assuming it.
The Five Traits That Make Cloud, Cloud
Not every hosted service deserves the label. The canonical definition lists five essential characteristics, and they are worth knowing because they double as a checklist when you evaluate a provider.
| Characteristic | What it means in practice |
|---|---|
| On-demand self-service | You provision capacity yourself, without filing a ticket |
| Broad network access | Resources are reachable over the network from many device types |
| Resource pooling | Hardware is shared across many customers via multi-tenancy |
| Rapid elasticity | Capacity scales up and down quickly, sometimes automatically |
| Measured service | Usage is metered, and billing follows consumption |
That last one matters more than people expect. Measured service is why cloud bills are variable and why cost surprises are so common. A team that treats cloud like a fixed-cost data center will get burned. If you want to get ahead of that, a clearer way to track cloud data transfer costs is worth reading before your first invoice arrives.
Service Models: Who Manages What
Public cloud comes in three main flavors, and the differences come down to how much the provider handles for you.
Infrastructure as a Service (IaaS) gives you virtual machines, storage, and networks. You manage the operating system and everything above it. It offers the most control and the most operational work.
Platform as a Service (PaaS) hands you a runtime for your code. The provider patches the operating system and scales the platform; you focus on the application.
Software as a Service (SaaS) delivers a finished product. You configure it and use it, and the provider runs everything underneath.
The practical mistake here is choosing IaaS by default because it feels familiar. Teams migrating from on-premises servers often lift their virtual machines straight into IaaS and then wonder why their operations burden barely changed. PaaS and managed services remove real work, but they require rewriting assumptions about patching, scaling, and state.
Regions, Zones, and Why Geography Is Architecture
Providers organize their footprint into regions, which are geographic areas, and availability zones, which are isolated clusters within a region designed to limit the blast radius of a failure. Put two copies of a workload in separate zones and a single data center outage should not take you down.
This is provider practice, not an international standard, and the naming, zone counts, and layouts change constantly. Treat any specific number you read as perishable.
Geography also drives cost and latency. Data that crosses a regional boundary usually incurs transfer fees, and users on the other side of the planet feel the delay. Two habits pay off: place workloads near the people who use them, and design so that chatty services sit close together. A guide on matching cloud regions to workload requirements covers the trade-offs in more depth, and if you are still deciding how to structure your footprint, this breakdown of when to split workloads across cloud accounts helps you avoid a single tangled environment.
The Shared Responsibility Model
Who secures what? The answer is split, and the split shifts depending on the service.
Under the shared responsibility model, the provider secures the cloud itself: physical facilities, hardware, the hypervisor, and the underlying network. The customer secures what they put in the cloud: identities, data, configurations, and application code.
The line moves. With IaaS, you own the operating system patches. With SaaS, the provider does. Most breaches traced to cloud environments come from customer-side misconfiguration, not provider failure, which is why identity and access management deserves more attention than it usually gets. Enterprise AI and cloud security guidance is a reasonable next stop if that is your priority.
There is no single standards-body definition of this split, so attribute it to whichever provider or government guidance you are relying on rather than treating it as universal law.
Standards and Assurance: What to Ask For
Because public cloud means trusting someone else’s controls, assurance matters. Two voluntary international standards come up often: one provides cloud-specific guidance for information security controls, and another addresses protection of personally identifiable information in public clouds acting as processors. Both are voluntary, not law, but they give you a shared vocabulary when auditing a provider.
Beyond certifications, ask about audit report availability, data residency commitments, deletion timelines at contract end, and subprocessors. The answers separate providers that have thought about enterprise risk from those that have not.
What Public Cloud Is Good At, and Where It Bites
Honest assessment beats enthusiasm. Public cloud excels at elasticity, global reach, and avoiding capital expense. It struggles with cost predictability, egress charges, and the operational discipline it demands.
| Strength | Corresponding risk |
|---|---|
| Fast provisioning | Sprawl and unused resources quietly billing |
| Global regions | Cross-region transfer fees and latency |
| Managed services | Lock-in to provider-specific APIs |
| Elastic scaling | Runaway spend during traffic spikes |
| No hardware ownership | Long-term cost can exceed owned infrastructure |
A common pattern: a team spins up a proof of concept, forgets to tear it down, and finds a line item three months later. Tags, budgets, and alerts are boring and they work. Set them on day one, not after the first surprise. (9481.org)
Practical Steps to Get Started Without Regret
- Inventory what you actually run today, including dependencies and data flows. A structured checklist of what to inventory before a cloud migration saves weeks later.
- Pick one small, low-risk workload first. Migrating a monolith wholesale is how projects stall.
- Define your identity model before deploying anything. Roles, groups, and least privilege are easier to design than to retrofit.
- Set budgets, tags, and alerts immediately.
- Decide your region and zone strategy with latency and data residency in mind.
- Document the shared responsibility split for each service you adopt, so nobody assumes someone else is patching.
The teams that succeed tend to treat cloud as an operating model change, not a hosting change. They invest in guardrails, automation, and cost visibility early. Those who struggle usually treat it as a lift-and-shift and inherit the same problems in a more expensive wrapper.
Conclusion
Public cloud works because virtualization turns expensive hardware into a flexible, metered utility that many customers can safely share. A hypervisor enforces separation, automation handles provisioning, and a global network of regions delivers it close to users. The provider secures the infrastructure; you secure everything you build on top of it.
Understanding the mechanics changes how you use the platform. You stop treating it like a rented data center and start designing for elasticity, isolation, and measured consumption. The technology is genuinely powerful. The discipline is what determines whether it pays off.
Frequently Asked Questions
Is public cloud the same as the internet?
No. The internet is the public network that connects systems worldwide. Public cloud is a set of rented computing resources reachable over that network. You can run a private cloud without touching the public internet, and you can use the internet without any cloud at all. The confusion comes from the word “public,” which in cloud terms refers to who can sign up, not to network openness. (What is cloud computing?)
How is public cloud different from private cloud?
Private cloud is dedicated to one organization, either on its own premises or hosted for it alone. Public cloud pools hardware across many customers. Private cloud offers more control and easier customization; public cloud offers faster scaling and lower upfront cost. Many organizations end up with a hybrid, keeping sensitive systems private while running variable workloads in public cloud. (Matching cloud regions to workload requirements) (Cloud computing)
Can multiple companies really share the same physical servers safely?
Yes, and it happens constantly. The hypervisor, virtual networking, and identity controls keep tenants separated. The risk is rarely the hypervisor itself; it is misconfiguration on the customer side, such as an accidentally public storage bucket. Sharing hardware is well understood. Sharing badly configured permissions is where trouble lives.
What happens to my data if I stop paying?
Policies vary by provider and contract. Most suspend access first, then retain data for a defined period before deletion. Some offer export windows; others do not. Read the termination clause before you migrate anything important, and keep independent backups of anything you could not afford to lose. Provider retention periods are not a backup strategy.
Does public cloud cost less than running my own servers?
Sometimes, and not automatically. Cloud wins when your demand is spiky or your workloads are small, because you avoid idle hardware. Owned infrastructure can win for steady, predictable, long-running workloads. The honest comparison includes staff time, egress fees, and the cost of the managed services you adopt along the way. Model it rather than assuming.
How do I keep cloud spending under control?
Four habits cover most of it: tag every resource so you know who owns it, set budgets and alerts before deploying, review idle and oversized resources monthly, and watch data transfer specifically because it is easy to miss. Cost problems are usually governance problems wearing a finance costume. Fix the process and the bill follows.